The CRA reporting clock is already running.
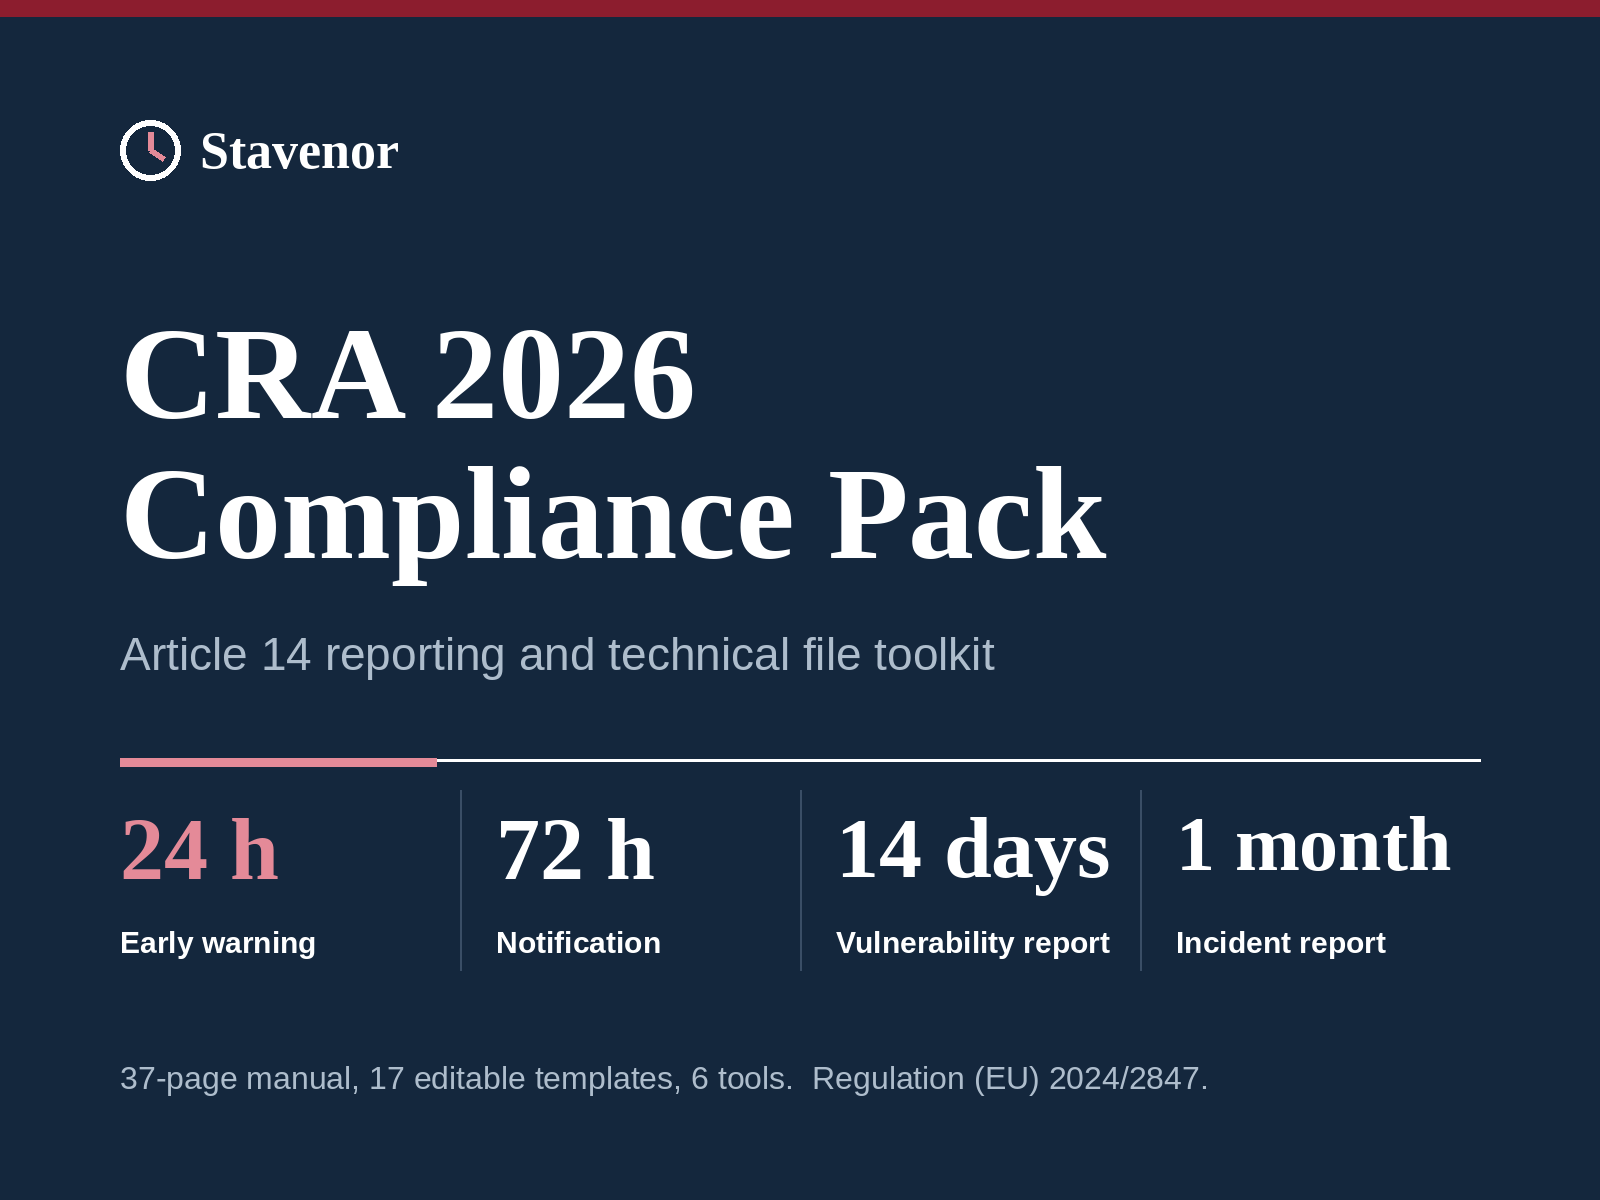
Since 11 September 2026, every manufacturer of a connected product sold in the EU must report actively exploited vulnerabilities and severe incidents. The first report is due within 24 hours. The CRA 2026 Compliance Pack gets you ready to file, and builds your technical file for December 2027.
Plus an intermediate report whenever the coordinating CSIRT asks for one. Article 14, Regulation (EU) 2024/2847.
The Regulation applies in full from 11 December 2027That is 0 days from today.
Four things most teams get wrong
- The 24-hour filing is not a one-line alert.
ENISA's platform requires eight fields at the early warning for a vulnerability, including a summary of up to 4,000 characters.
The early warning, field by field - Your installed base is in scope.
Reporting applies to products you placed on the market before December 2027, modified or not.
Products already on the market - Reporting outlives support.
Vulnerability handling ends with the support period. The duty to report does not.
The support period - A vulnerable library is not always reportable.
Under the Commission's guidance, it is reportable when it has been exploited in your product.
Third-party components
What's in the pack
25 files. Word, Excel, PDF and Markdown. Delivered instantly.
- Operating manual
- 37 pages in eleven parts, from deciding whether the CRA applies to you, to the roadmap for 11 December 2027.
- 17 templates
- Every Article 14 filing form, built from all 39 fields of ENISA's reporting platform, with each field's character limit and required status. The internal procedure that defines when you became aware. A publishable vulnerability disclosure policy. The Annex I conformity matrix, the technical file index and the EU declaration of conformity.
- 6 tools
- A gap analysis of 82 controls, a 90-day plan, a RACI matrix, a printable classification tree, a printable reporting clock for your on-call engineer, and the verification register.
See inside the pack
A one-minute walkthrough of the real files you receive. No sound.
Built from the sources, and it shows its working
Free CRA templates exist. Most are built from summaries of summaries. This pack was built from the text of the Regulation in the Official Journal, ENISA's own platform specifications and the European Commission's guidance.
Every one of its 124 regulatory claims is listed in a register with its source and a verification status, so you can check any line yourself. Along the way it corrects 19 errors that are widely repeated elsewhere. Where something is genuinely uncertain, the pack says so and tells you who to ask.
Free guides
Start here
- What Is the Cyber Resilience Act? A Plain-Language Introduction for Manufacturers
The EU Cyber Resilience Act explained simply: who it applies to, what manufacturers must do, the key dates up to December 2027, and where to start.
- CRA Annex I: The 22 Essential Requirements in Plain Language
All 22 essential cybersecurity requirements of the Cyber Resilience Act's Annex I, explained one by one: 14 for the product, 8 for vulnerability handling.
Reporting under Article 14
- CRA Article 14: The 24-Hour Early Warning, Field by Field
Since 11 September 2026, CRA Article 14 requires a 24-hour early warning. What ENISA's platform actually asks for, when the clock starts, and the three traps.
- ENISA SRP for the CRA: Registration, Roles and the Rules That Trip People Up
How ENISA's CRA reporting platform works: Primary and Secondary AR roles, verification, 7-day invitations, private drafts and the rules that trip people up.
- ENISA's CRA Reporting Platform: What the 72-Hour and Final Reports Require
Field by field: what ENISA's Single Reporting Platform requires in the CRA 72-hour notification and the final reports, with every character limit.
- When Does a Manufacturer 'Become Aware' Under the CRA?
Every CRA Article 14 deadline runs from the moment you become aware. The Commission's guidance defines it — and closes the loophole of delaying the assessment.
- CRA Severe Incident: The Two Tests of Article 14(5)
When is an incident 'severe' under the Cyber Resilience Act? Article 14(5) has two alternative tests — and most summaries leave out the second one.
- CRA Article 14(6): The Intermediate Report Nobody Plans For
Beyond the 24-hour, 72-hour and final reports, the CRA lets the coordinating CSIRT request an intermediate report — with a deadline it sets. What to prepare.
- Vulnerability in a Third-Party Component: Do You Have to Report It Under the CRA?
A library in your product is vulnerable. Must you notify under CRA Article 14? The Commission's guidance gives a clear test: was it exploited in your product?
Vulnerability handling and user information
- CRA Coordinated Vulnerability Disclosure: What Annex I Requires
The Cyber Resilience Act requires a coordinated vulnerability disclosure policy. What Annex I asks for, how to make it findable, and a free template.
- CRA SBOM Requirements: What Annex I Actually Asks For
Does the Cyber Resilience Act require an SBOM? Yes. What Annex I says about format and depth, whether it must be public, and who can ask to see it.
- CRA User Information: The Nine Items of Annex II
What the Cyber Resilience Act requires you to tell the users of your product: all nine items of Annex II, the support end date, and three traps.
- CRA Support Period: Why Five Years Is Not the Default
The CRA sets a minimum five-year support period. The Commission says plainly that five years is not the default. What Article 13(8) really requires.
Scope, classification and the technical file
- Does the CRA Apply to Products Already on the Market?
Products sold before December 2027 escape most CRA requirements — but not the reporting obligations. Article 69(3) explained, with the Commission's guidance.
- When Is the Cloud Part of Your Product Under the CRA?
Under the Cyber Resilience Act, a cloud backend can be part of your product. The Article 3 test, recital 12's smart home example, and what stays out of scope.
- CRA Important Products: Class I, Class II and the Core Functionality Test
Is your product in CRA Annex III? All 19 Class I and 4 Class II categories, the core functionality test, and what each class means for conformity.
- CRA Technical Documentation: The Annex VII Checklist
The eight items Annex VII of the Cyber Resilience Act requires in your technical file — plus when it must exist, how long to keep it, and in what language.
- CRA Fines: The Three Penalty Tiers of Article 64
Cyber Resilience Act fines reach €15 million or 2.5% of worldwide turnover. How the three tiers of Article 64 work, and which breach falls where.
Is it for you?
Made for
- Manufacturers of connected devices, especially embedded Linux
- Teams under 50 people, without a compliance department
- Products on the Module A self-assessment route
Not made for
- Class II and critical products, which need a notified body. The reporting parts still apply to you.
- Large organisations with an in-house compliance function
- Anyone looking for legal advice. This is documentation, not counsel.
- 25 files, instant download
- Single-organisation licence for internal use
- Edition 2026.1, legal position as at 20 September 2026. No updates included.
- Self-service. No support, not legal advice.
Questions before you buy
Will this make my product CRA-compliant?
No document can. The pack gives you the method, the structure of every decision, and forms built to the exact platform and regulatory specifications. The decisions are yours, and so is the compliance.
Is this legal advice?
No. It is self-service documentation. Where the Regulation raises a question only a lawyer can answer, the pack says so.
How do I download it?
After payment you receive an email from Lemon Squeezy. Click "Download your files" and confirm your email address when asked: Lemon Squeezy sends you a sign-in link or code. No password needed.
Do I get updates?
No updates are included. You buy Edition 2026.1, with the legal position as at 20 September 2026. The verification register lists every source and when it was read, so you know what to re-check.
My product is Class II or critical. Is this useful?
Partly. The reporting obligations are the same for every product, so the reporting forms and procedure apply in full. The self-assessment route covered in the rest of the pack does not apply to you.
What formats are included?
PDF, Word, Excel and Markdown. They open in Microsoft Office, Google Workspace, LibreOffice or any text editor.
Can I use it for my clients?
No. The licence covers internal use by a single organisation.
What about refunds?
Purchases are processed by Lemon Squeezy as merchant of record, under its buyer terms.
Is support included?
No. Everything is designed to be used on your own, including the list of what could not be verified and where to check it.